Pantheon release notes

Your destination for staying informed about our latest innovations and product updates.
Subscribe to RSS feed

Security
October 14, 2026

The latest security update for Next.js addresses three vulnerabilities in upstream dependencies: two critical vulnerabilities and one high-severity vulnerability.

Action required

Because this is a security update, we recommend that customers update affected Next.js applications as soon as possible. Customers are responsible for updating their application dependencies and redeploying; Pantheon does not update Next.js sites on customers' behalf.

The published Next.js advisory lists 16.4.1 and 15.5.28 as patched versions.

If your application directly manages React Server Components packages, update them to the patched versions listed in the React advisories: 19.0.9, 19.1.10, 19.2.9, or 19.3.1, as applicable.

Highlights

This update addresses three upstream security vulnerabilities:

  • Critical — Remote code execution in image processing: A vulnerability in the upstream image-processing stack can lead to remote code execution when Next.js processes SVG files on glibc-based Linux systems. The advisory identifies Next.js 15.5.28 and 16.4.1 as patched versions. As a workaround, use Sharp 0.35.5 or later. See GHSA-2464-fhr4-w9xw.
  • Critical — React Flight remote code execution: Crafted React Server Component payloads can lead to remote code execution in rare cases involving multiple typed arrays and attacker-controlled values. See GHSA-xqc2-xf4c-x3h3.
  • High — Denial of service through Server Functions: Crafted requests to Server Function endpoints can cause excessive CPU use or out-of-memory exceptions. Applications that do not use server-side React or a framework that supports React Server Components are not affected. See GHSA-h3gv-c5rc-p453.

For full technical details and affected package versions, review the linked security advisories.
October 14, 2026

Drupal core security release SA-CORE-2026-014 (CVE-2026-108097, risk 19/25) is now available. It fixes a critical remote code execution vulnerability in the Field UI module. Drupal core alone is not directly exploitable, but several exploit paths exist through contributed modules, and at least one does not require authentication. Custom code can also expose the vulnerable functionality.

Action required

Update your Drupal sites to a patched release as soon as possible.

  • Drupal 11.4.10
  • Drupal 11.3.19
  • Drupal 10.6.19

Drupal 12.0.0-alpha1 through 12.0.0-beta1 are also affected. See the security advisory for Drupal 12 fix details.

Drupal 11.2.x and earlier, Drupal 10.5.x and earlier, Drupal 9, and Drupal 8.9 are end-of-life. They are affected and do not receive a patch. Upgrade these sites to a supported release.

Drupal 7 sites on Pantheon receive this fix through Drupal 7 long-term support. See the Drupal 7.107 release note.

To apply the update, use one-click core updates in the Pantheon dashboard.

Mitigation until you update

If you cannot update right away, uninstall the core Field UI module (field_ui). The Drupal Security Team states this protects your site until you update.

As a founding Platform Partner of the Drupal Steward program, Pantheon provides protection against some known attack vectors. Steward does not cover all possible exploits, so update your site.

October 14, 2026

As part of Pantheon's Long-Term Support (LTS) for Drupal 7, Drupal 7.107 is now available with a backported security patch.

This release backports the fix for SA-CORE-2026-014 (CVE-2026-108097), a critical remote code execution vulnerability in the Field UI module. Drupal core alone is not directly exploitable, but several exploit paths exist through contributed modules, and at least one does not require authentication.

Action required

Apply the latest upstream update to your Drupal 7 site to receive this fix. See related documentation for how to apply core updates.

This fix changes how Field UI overview tables assign rows to regions: Drupal core no longer calls the #region_callback function set on a table row. After you update, review whether any custom code uses #region_callback, and test the Manage fields and Manage display pages to confirm the Field UI tables work as expected.

About Drupal 7 long-term support

Pantheon has partnered with Tag1 Consulting to deliver security updates and maintenance for Drupal 7 sites. This extended support is included at no additional cost.

For configuration guidance and detailed information, visit our related documentation.

October 6, 2026

The latest security release for WordPress, 7.1.3, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.1.3 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has deployed a platform-wide mitigation (virtual patching via our routing network) against external abuse of the stored XSS on the Comments administration page, and is actively monitoring that rule. However, customers need to update their sites as soon as possible.

Highlights

This release resolves seven security vulnerabilities:

  • A stored XSS on the Comments administration page, exploitable via pending comments.
  • A DoS issue in the WP_Http::make_absolute_url() method.
  • A second-order SQL injection in WordPress WXR export.
  • A weakness allowing Author role users to sticky posts.
  • Unauthenticated disclosure of comments on private and unpublished posts.
  • Imgur embeds are vulnerable to XSS.
  • Forgeable parameters passed to the {status}_{type} hook can lead to action name collision.

For full details, see the WordPress 7.1.3 release notes and WordPress documentation.

September 30, 2026

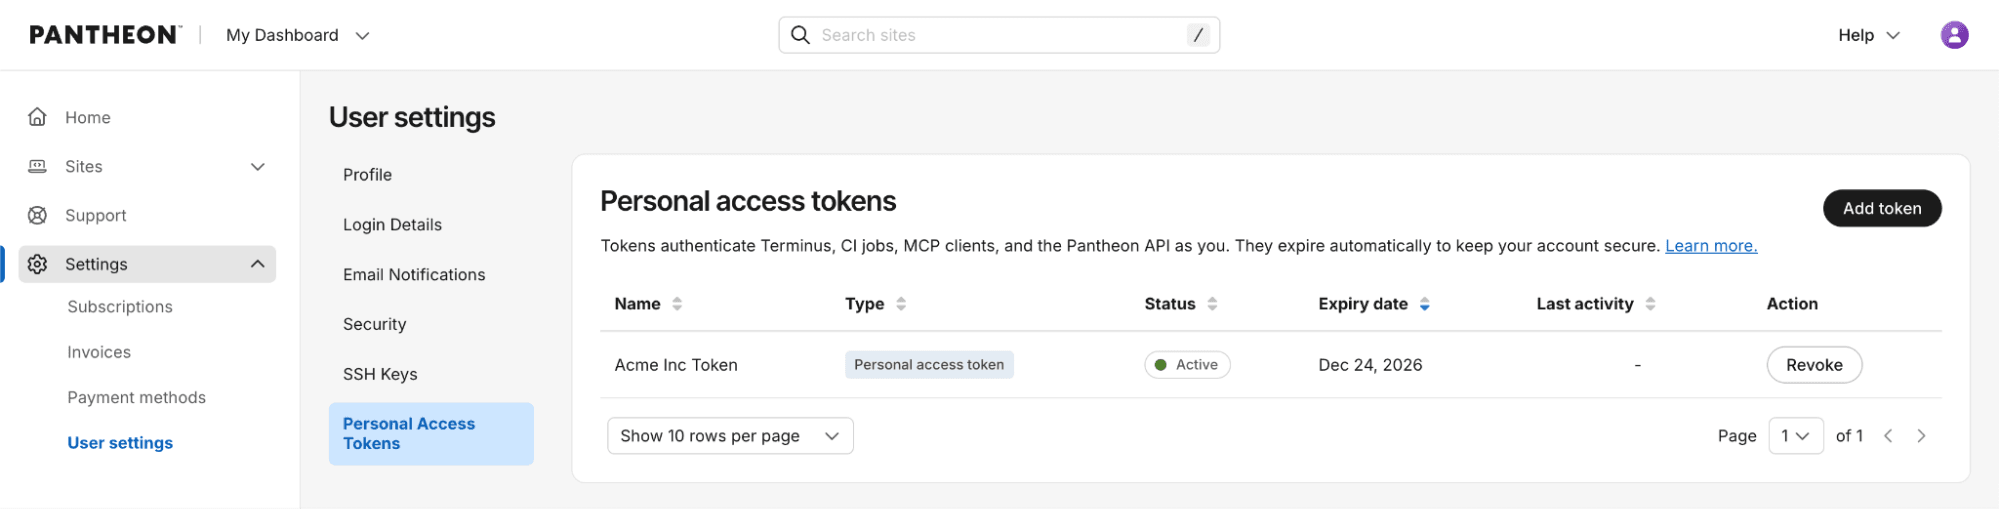
Pantheon is renaming machine tokens to personal access tokens (PATs) and adding stronger security controls with automatic expiration.

What’s changed

  • Time-bound credentials: New PATs expire 90 days after creation, reducing the risk of credentials that remain valid indefinitely.

What hasn’t changed

  • Continue using the same Terminus flow and commands for authentication, listing, and deleting tokens.
  • Continue to create and revoke tokens in the dashboard under your User settings.

What this means for legacy machine tokens

Existing machine tokens continue to work and are not changed by this release. No immediate action is required. Machine tokens are now considered a legacy authentication method, so we recommend using personal access tokens for new integrations and workflows.

If you adopt a PAT, plan to renew it every 90 days and update the corresponding secret wherever the token is used.

Get started

Create a new personal access token from User settings → Personal Access Tokens, copy it once, store it securely, and use it with your existing Terminus authentication workflow.

Dashboard interface showing new personal access tokens

For more details, see related documentation.

September 25, 2026

PHP versions 8.2.34, 8.3.35, 8.4.26, and 8.5.11 are now available on the platform. These updates include important security fixes, along with bug fixes and enhancements that improve performance and stability.

The security fixes include a high-severity issue in the SOAP extension (CVE-2026-91765), plus fixes in OpenSSL certificate verification, the HTTP stream wrapper, and PHP-FPM.

Updates will be applied automatically over the next few days, so no manual action is required. See PHP versions on Pantheon to check or change your site's PHP version.

September 22, 2026

The latest security release for WordPress, 7.1.2, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.1.2 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has pre-deployed platform-wide mitigations (virtual patching via our routing network) against external abuse of this vulnerability (CVE-2026-87902), and is actively monitoring those rules. However, customers need to update their sites as soon as possible.

Highlights

This release resolves one critical severity vulnerability (CVE-2026-87902) that does not require authentication to exploit. Under certain server and theme conditions, an unauthenticated attacker can cause page template resolution to include a chosen readable local PHP file outside the active theme directories, which could potentially lead to remote code execution.

For full details, see the WordPress 7.1.2 release notes and WordPress documentation.

September 18, 2026

The latest security release for WordPress, 7.1.1, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.1.1 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has pre-deployed platform-wide mitigations (virtual patching via our routing network) against external abuse of some of these vulnerabilities, and are actively monitoring those rules. This includes an unauthenticated stored cross-site scripting vulnerability (CVE-2026-93485), reported through Patchstack's Vulnerability Disclosure Program, which was already covered by these mitigations ahead of the release. However, customers need to update their sites as soon as possible.

Highlights

This release resolves 11 security vulnerabilities, most requiring an authenticated role (Contributor or above) to exploit. WordPress has not assigned CVE identifiers to these issues.

For full details, see the WordPress 7.1.1 release notes and WordPress documentation.