Pantheon release notes

Your destination for staying informed about our latest innovations and product updates.
Subscribe to RSS feed

August 18, 2026

Pantheon MU-Plugin 1.5.7 adds dismiss and hide controls for the Pantheon WordPress core update notice ("A new WordPress update is available!"). Apply upstream updates to get this version of the mu-plugin.

Dismiss the notice

Any user who sees the notice can dismiss it with the X in the corner. The dismissal is saved per user, so it persists across page loads and logins. The notice reappears only when a newer WordPress version becomes available.

Hide the notice

To hide the notice more permanently, or for everyone, you can:

  • Target #pantheon-update-notice (or the .pantheon-update-notice class) with CSS.
  • Return false from the pantheon_show_update_notice filter.
  • Define the PANTHEON_SHOW_UPDATE_NOTICE constant as false in wp-config.php.

For details, see Suppress WordPress Admin Notice.
August 17, 2026

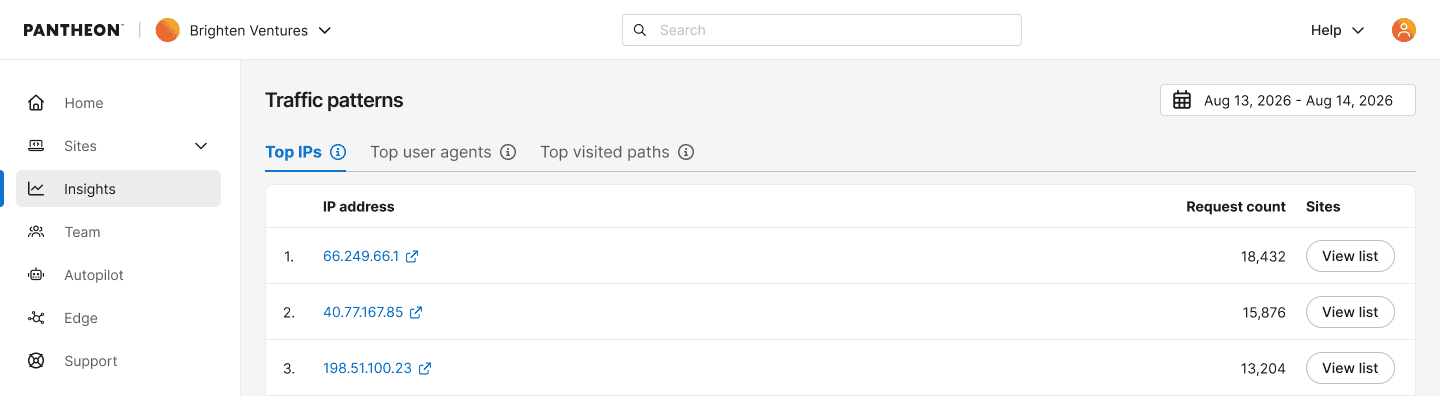
Pantheon has extended traffic visibility on the dashboard – you can now see aggregated traffic insights across your entire workspace, giving portfolio managers and agencies a single view of what's happening across all their sites.

  • Workspace Top IPs, User Agents, and Visited Paths: New tabs on the workspace Insights page show the top IP addresses, user agents, and visited paths generating traffic across every site in your workspace – no need to check each site individually to spot patterns.
  • Drill-Down by Site: Click into any row to see which specific sites are driving that traffic, so you can quickly pinpoint where to focus your attention.
  • User Agent Parsing: Instantly see a parsed breakdown of any user agent to help you confirm whether high-volume traffic is a real visitor or something worth investigating further.
  • IP Investigation: Click any IP address to open its AbuseIPDB report so you can quickly assess whether it has a history of malicious activity.

For more details, see related documentation.

Information:
Note

This feature is only available for sites that have migrated to our next-generation Global CDN. If your workspace includes sites still on our legacy Global CDN, your insights data will only reflect the migrated sites.

If you have not started or completed your migration, visit our documentation to get started.

top IPs

August 17, 2026

What's new

You can now choose how the Pantheon Dashboard looks. Alongside the classic Light appearance, the Dashboard supports a full Dark mode, plus a System option that automatically follows your device or browser's own light/dark setting.

Pick your preference from the Theme control in your User Menu:

  • Light — the classic Dashboard appearance (default)
  • Dark — a full dark color scheme across the Dashboard
  • System — automatically matches your OS or browser's current preference, and updates live if that setting changes

Your choice is saved to your account, so it follows you across devices and browsers — no need to set it again each time you log in somewhere new. If you haven't set a preference, the Dashboard defaults to Light.

Why it matters

Dark mode reduces eye strain in low-light environments, can save battery on some devices, and matches how many people prefer to work. If that preference is already set at the OS level, System mode picks it up automatically — no extra effort required.

Where to find it

Look for the Theme option in your User Menu at the top of the Dashboard. For more details, see related documentation.

August 14, 2026

All Pantheon-maintained Drupal modules and WordPress plugins have been confirmed compatible with PHP 8.5. Some required code updates and received new releases; others were already compatible.

Drupal modules

The following Drupal modules have been updated for PHP 8.5 compatibility:

WordPress plugins

The following WordPress plugins have been updated for PHP 8.5 compatibility:

To switch your site to PHP 8.5, see Upgrade PHP Versions.

August 13, 2026

Pantheon has released version 2.3.4 of the WP SAML Auth WordPress plugin.

Version 2.3.3 was released on August 11, 2026 with a security fix for SAML user matching. The 2.3.3 package published to the WordPress Plugin Repository was missing its vendor directory, which includes the bundled onelogin/php-saml library, so sites that took that update could not authenticate through SAML. Version 2.3.4 was released the following day to correct the packaging, and it carries the 2.3.3 security fix as well. Both releases are one day apart, so a site may be on either version depending on when it last updated.

Warning:
Action required

Update to 2.3.4 as soon as possible. Sites running 2.3.2 or earlier are missing a security fix, and sites that updated to 2.3.3 from the WordPress Plugin Repository may be unable to log in through SAML.

What's new

  • Security: user matching now accent-sensitive — Fixes an account takeover where an accent-insensitive database collation could match a SAML attribute to the wrong WordPress user. User lookup is now verified with a case-insensitive, accent-sensitive comparison. Originally released in 2.3.3.
  • Restores the bundled SAML library — The vendor directory, which includes onelogin/php-saml, is included in the package again. Sites affected by 2.3.3 will be able to authenticate through SAML after updating.

Who is affected

  • Sites on 2.3.2 or earlier are missing the security fix and should update to 2.3.4.
  • Sites on 2.3.3 installed from the WordPress Plugin Repository, using the WordPress dashboard, WP-CLI, or the direct download, have the security fix but may be unable to authenticate through SAML. Update to 2.3.4 to restore login.
  • Sites that install the plugin with Composer are unaffected by the packaging issue, because onelogin/php-saml is resolved as a dependency rather than from the bundled copy. These sites should still update to 2.3.4 if they are on 2.3.2 or earlier.

Update to 2.3.4 from the WordPress dashboard under Plugins > Installed Plugins, or download it from the WordPress Plugin Repository.

For more details, see the plugin release notes.

August 12, 2026

The latest security release for WordPress, 7.0.4, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.0.4 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has pre-deployed platform-wide mitigations (virtual patching via our routing network) against external abuse of the vulnerability, and are actively monitoring those rules. However, customers need to update their sites as soon as possible.

Highlights

This update resolves a security vulnerability:

For more information on this release, please see the WordPress documentation.

August 7, 2026

You can now update the credentials for a Custom Upstream directly from the Pantheon Dashboard — no support ticket or new upstream required. Previously, changing a private repository's access token meant either creating a new Custom Upstream and switching each site over to it, or contacting Pantheon Support.

What's new

  • The upstream Settings page now has a Repository credentials section that shows whether credentials are set and lets you update them — a GitHub personal access token or a Bitbucket repository access token.
  • The stored credential is masked and never displayed back in the Dashboard.

Changing the repository URL still requires creating a new Custom Upstream.

For steps, see Edit an Existing Custom Upstream.

August 6, 2026

The latest security release for WordPress, 7.0.3, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.0.3 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has pre-deployed platform-wide mitigations (virtual patching via our routing network) against external abuse of the vulnerability, and are actively monitoring those rules. However, customers need to update their sites as soon as possible.

Highlights

This update resolves a number of security vulnerabilities, including:

The RCE vulnerability is serious, but unlike wp2shell it requires specific targeting of a user to be effective. However, it is present on all versions of WordPress going back to 4.7.

Backports

Backport patches for older branches of WordPress have been published to our WordPress upstream. Customers on an older branch should update to the patched release for their branch:

6.9.6, 6.8.7, 6.7.6, 6.6.6, 6.5.9, 6.4.9, 6.3.9, 6.2.10, 6.1.11, 6.0.13, 5.9.15, 5.8.14, 5.7.16, 5.6.18, 5.5.19, 5.4.20, 5.3.22, 5.2.25, 5.1.23, 5.0.26

For more information on this release, please see the WordPress documentation.