Pantheon release notes

Your destination for staying informed about our latest innovations and product updates.
Subscribe to RSS feed

October 6, 2026

The latest security release for WordPress, 7.1.3, is available on Pantheon.

Action required

Because this is a security update, we recommend all users upgrade to WordPress 7.1.3 as soon as possible from your Pantheon dashboard or Terminus to access the latest features, fixes, and security enhancements. See related documentation for how to apply core updates.

Pantheon has deployed a platform-wide mitigation (virtual patching via our routing network) against external abuse of the stored XSS on the Comments administration page, and is actively monitoring that rule. However, customers need to update their sites as soon as possible.

Highlights

This release resolves seven security vulnerabilities:

  • A stored XSS on the Comments administration page, exploitable via pending comments.
  • A DoS issue in the WP_Http::make_absolute_url() method.
  • A second-order SQL injection in WordPress WXR export.
  • A weakness allowing Author role users to sticky posts.
  • Unauthenticated disclosure of comments on private and unpublished posts.
  • Imgur embeds are vulnerable to XSS.
  • Forgeable parameters passed to the {status}_{type} hook can lead to action name collision.

For full details, see the WordPress 7.1.3 release notes and WordPress documentation.
October 6, 2026

Pantheon is introducing the official Pantheon MCP Server, a governed way to let compatible AI agents operate on your Pantheon fleet through the platform API.

The MCP server exposes Pantheon operations as agent tools, mostly read-only, with any action that changes something requiring your approval in your AI client. It forwards the user's own Pantheon identity, so an agent can only reach what that user already can.

What's included

  • A stateless MCP server that maps Pantheon operations to agent tools, covering workspaces, sites, environments, builds and deploy status, runtime logs, secrets, and upstreams, with no delete capabilities in this beta.
  • Authorization stays with Pantheon: the server forwards the user's own token and the platform decides what that token may see and do.

Who it's for

Developers and teams using compatible AI coding agents who want to manage Pantheon sites and environments through agent workflows while keeping control of what agents can change.

How to get started

Connect from Claude Desktop, Web, or Code using the Pantheon MCP listing. Sign in with your normal Pantheon account through the OAuth flow; the client stores your token securely. Disconnect from the Pantheon MCP in the client to log out.

Support for more AI agents is coming soon.

For more details, see related documentation.

Availability

All Pantheon customers. For feedback, please sign up for the Pantheon Community Slack here if you don't already have an account and join us in the #beta-mcp-server channel.

October 6, 2026

Pantheon is opening the Beta of the Public API v1, a stable, Auth0-secured REST API for automating platform operations across your fleet.

The Public API v1 gives partners, DevOps teams, and agencies a documented, contract-stable way to run Pantheon operations programmatically. It extends the earlier alpha with expiring tokens and an OpenAPI 3.x schema that Pantheon commits to through GA.

What's included

  • Auth0-secured authentication with expiration, replacing full-grant session tokens.
  • Full operational surface: site, environment, backup, domain, and workflow operations.
  • Initial capabilities: Upstream, Secrets Manager, access to Next.js build and runtime logs, and more.
  • Published as an OpenAPI 3.x schema, so you can generate first-class clients directly.
  • v1 contract stability, committed through GA.

Who it's for

Technology partners embedding Pantheon in their own products, enterprise DevOps teams standardizing across many sites, agencies building client dashboards, and regulated-industry customers who require expiring tokens.

How to get started

The API is served at api.pantheon.io under /v1. Interactive docs are at /docs and the OpenAPI spec at /v1/openapi.json. Authenticate with your own Auth0-issued token.

For more details, see related documentation.

Alpha (v0) users

The v0 API keeps running for about 60 days after today's Beta release of v1, then shuts down. The /v1 endpoints reject legacy machine tokens, so move to personal access tokens.

Availability

All Pantheon customers. For feedback, please sign up for the Pantheon Community Slack here if you don't already have an account and join us in the #beta-public-api channel.

October 6, 2026

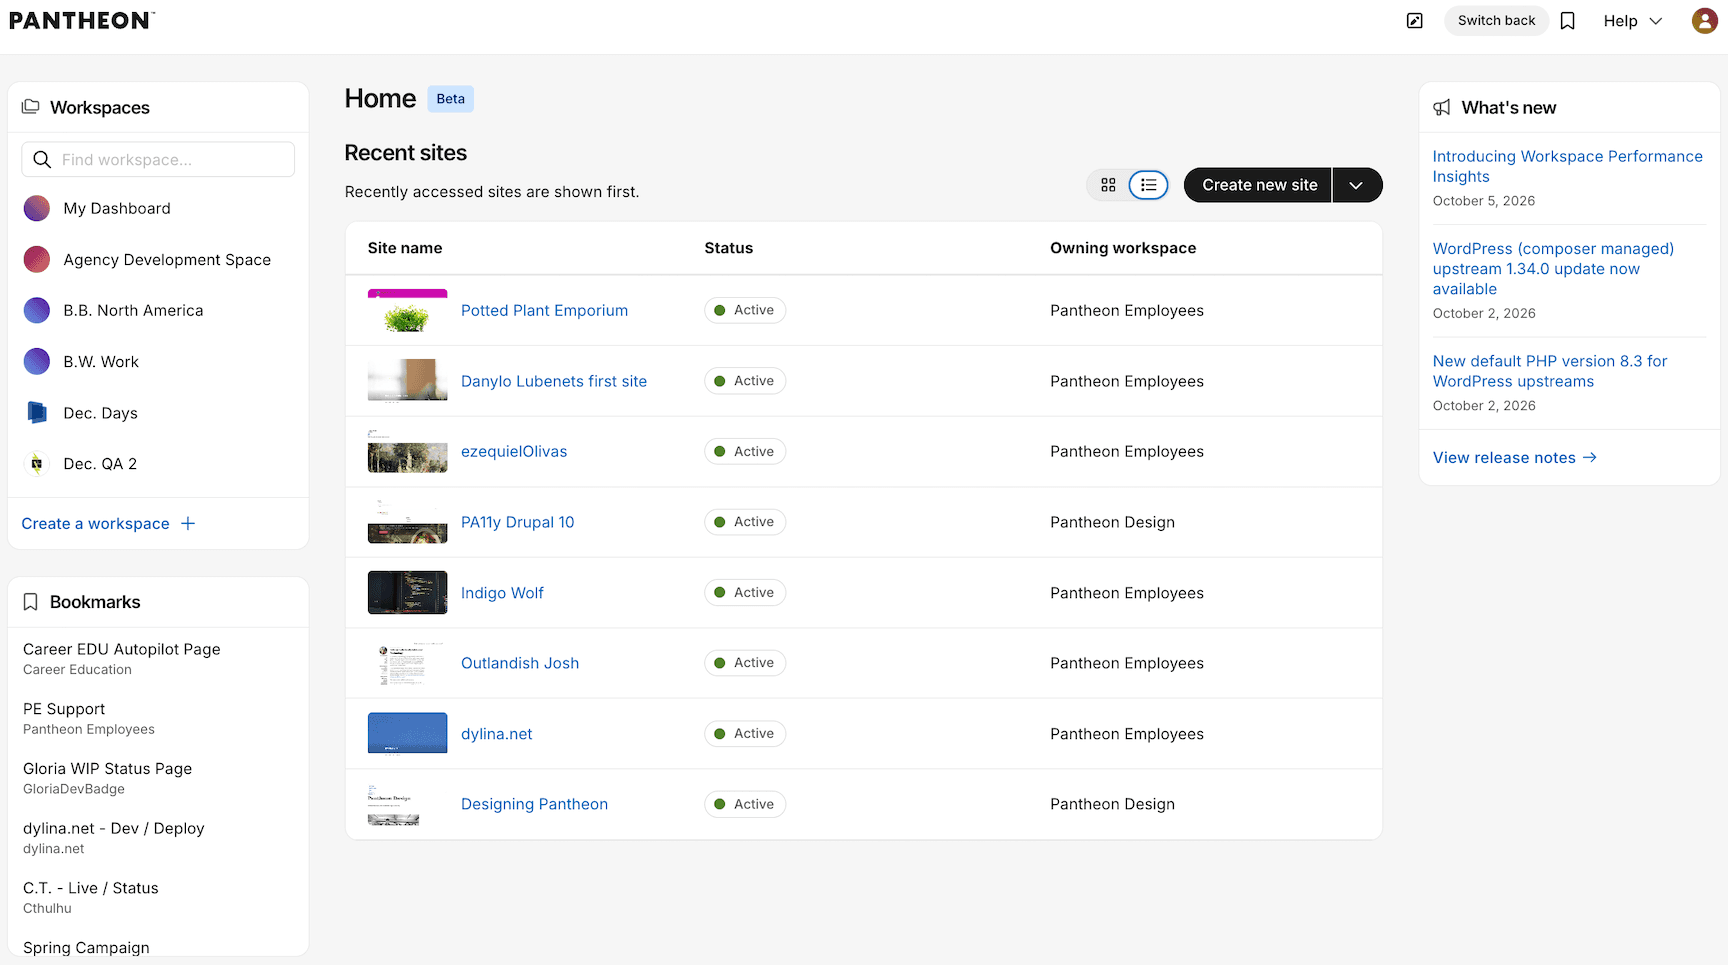
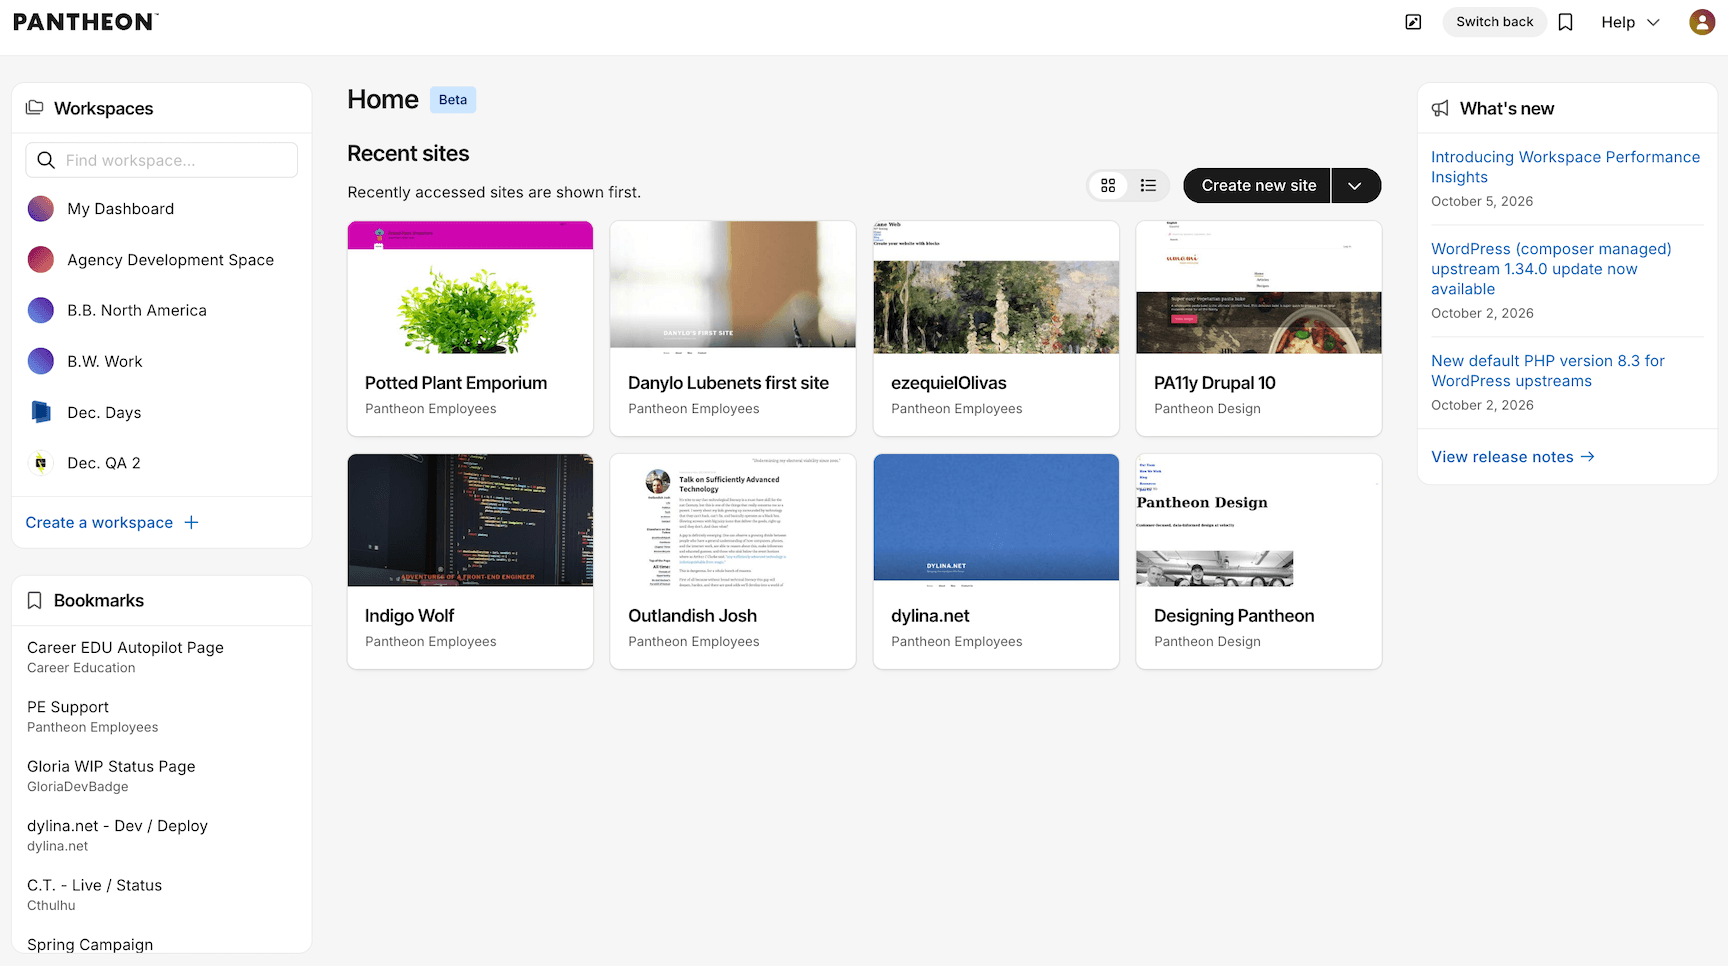
Pantheon’s new dashboard home experience is now available in beta. It gives you a more useful starting point for finding your sites, accessing frequently used pages, and staying up to date with Pantheon.

Recent Sites are available in a card view:

Home in card view

What’s new

  • A new Home experience - Get a single view of your Recent Sites across all of your workspaces.
  • Card or list view - Choose how you want to browse Recent Sites. List view also shows each site’s status and owning workspace.
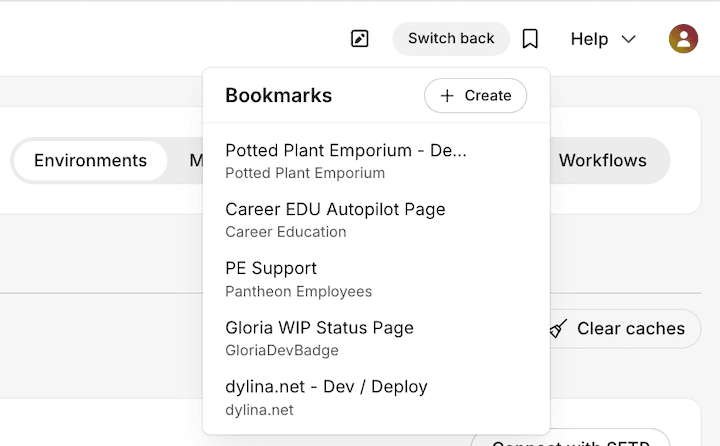
  • Bookmarks capability - Create and access bookmarks for your frequently visited pages from Home and dashboard navigation.
  • Release notes in the dashboard - See the latest Pantheon product updates directly from the Home experience.
  • Refreshed Workspace Overview - Workspace Overview has a visual refresh and now supports the same card and list views for Recent Sites.

Switch to list view to see site status and owning workspace:

Home in list view

Open the Bookmarks panel to quickly access saved pages:

Bookmarks panel

How to try it

The new experience is available to all dashboard users, but you’ll continue to land on the current dashboard experience by default. Select Try the new dashboard to opt in to the beta. You can select Switch back at any time to return to the current experience.

October 5, 2026

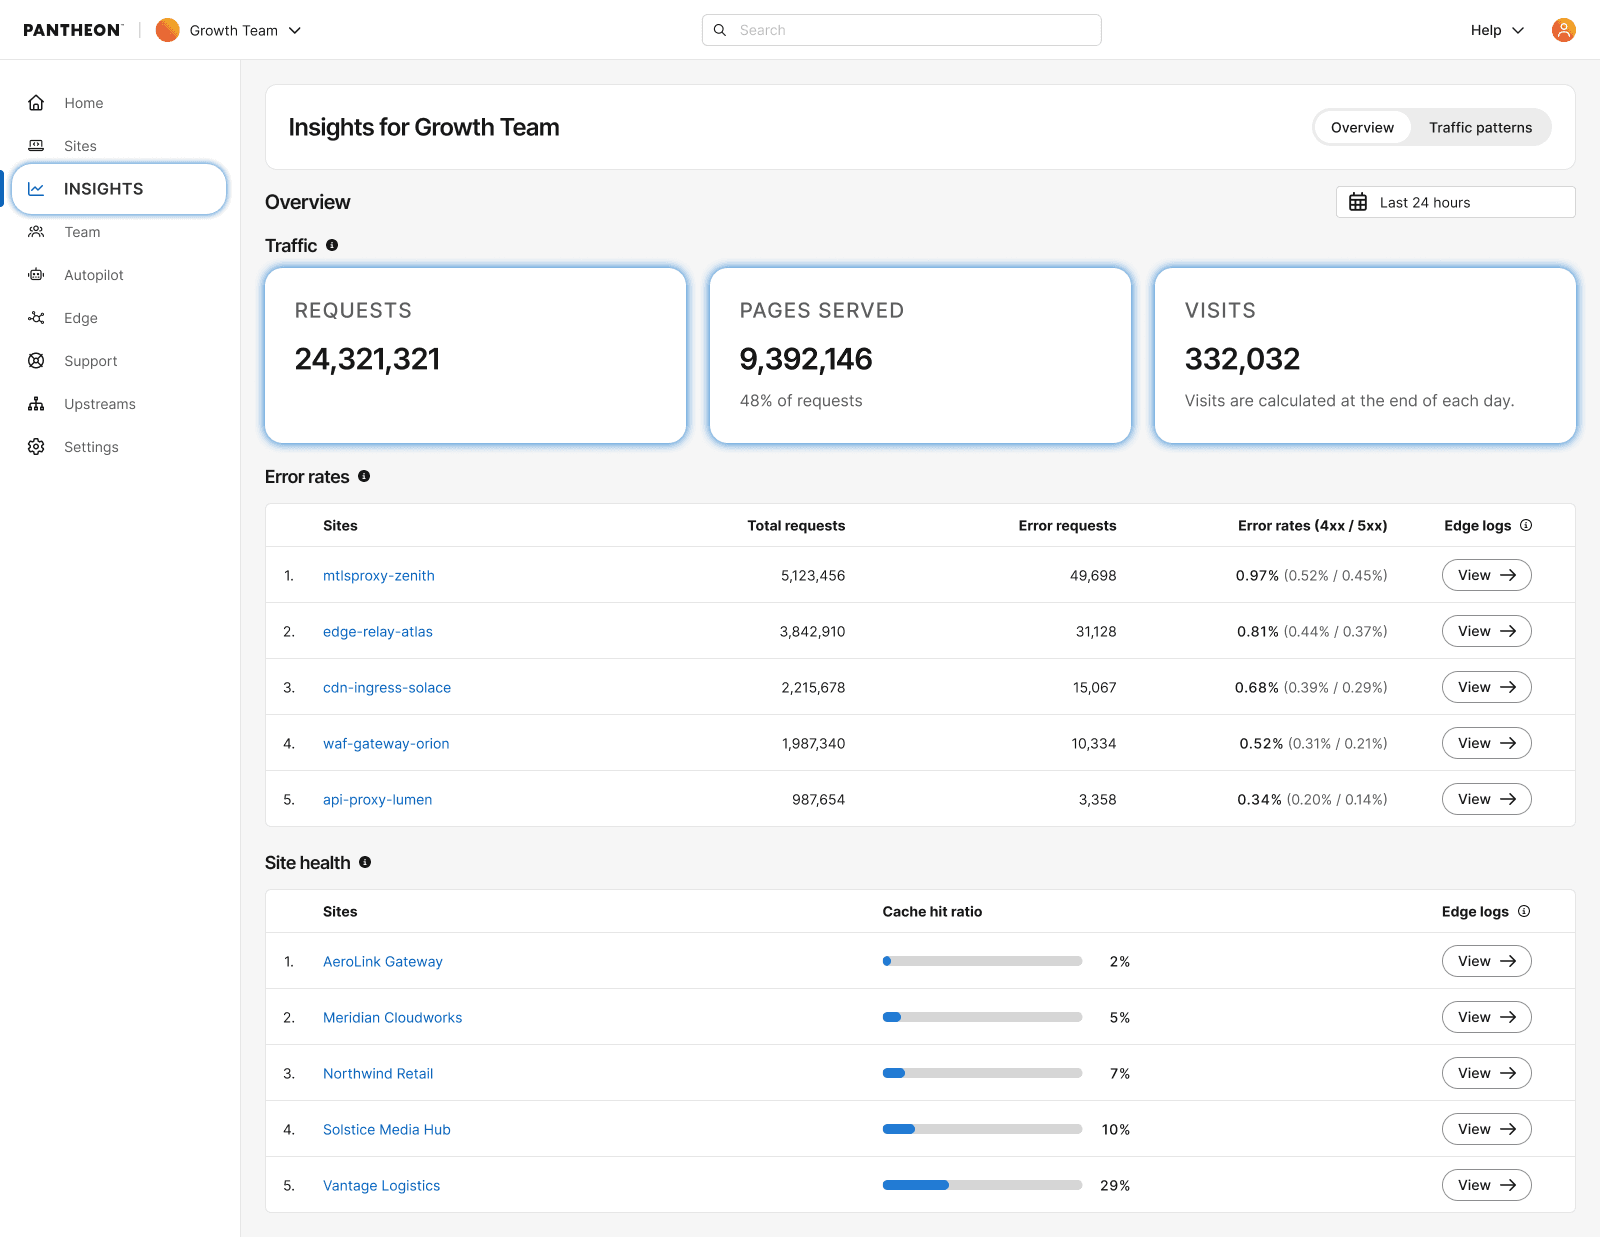
Pantheon has added workspace-level performance visibility to the Workspace dashboard – you can now see which sites in your workspace need attention without checking each site dashboard individually.

  • Error Rates: A new view on the workspace Insights page ranks your sites by error rate, so you can quickly spot which sites need updates or deeper investigation.
  • Caching Health: See which sites are seeing degraded cache performance across your entire workspace at a glance.

Click through from a flagged site directly to use deeper troubleshooting tools on its site dashboard.

workspace performance insights showing traffic, site health and error rates

Information:
Note

This feature requires your site to be on our next-generation Global CDN. If your workspace includes sites still on our legacy Global CDN, your performance overview will only reflect migrated sites.

If you have not started or completed your migration, visit our documentation to get started.

October 2, 2026

The 1.34.0 update is now available for the WordPress (composer managed) upstream. This update changes the default PHP version to 8.3, syncs the upstream with Roots Bedrock, and fixes a PHP warning. The Bedrock sync changes the Composer repository defaults, which can cause merge conflicts in your composer.json file.

Updates

  • Updates the default PHP version to 8.3 and changes the PHP requirement in composer.json to >=8.3. For more information about the PHP default change, see New default PHP version 8.3 for WordPress upstreams. (For more information see #204.)
  • Syncs the upstream with Bedrock. (For more information see #201.) This includes:
    • Changing the Composer repository from WPackagist (wpackagist.org) to WP Packages (repo.wp-packages.org). Package names for plugins and themes change from wpackagist-plugin/* and wpackagist-theme/* to wp-plugin/* and wp-theme/*.
    • Removing the roots/wp-password-bcrypt package from composer.json.
    • Setting WP_ENVIRONMENT_TYPE from WP_ENV when it is not already defined, and setting WP_DEVELOPMENT_MODE when it is configured.
    • Setting MYSQL_CLIENT_FLAGS to use SSL when DB_SSL is set.

Bug fixes

  • Resolves a rtrim() warning in PHP 8.1 and later environments. (For more information see #189. Props @mattmacneil.)

For more details, refer to the WordPress (Composer Managed) changelog.

Action required

To benefit from these updates and ensure your site is using the most current version, apply the update to your WordPress (composer managed) site or custom upstream.

If your composer.json file requires plugins or themes using wpackagist-plugin/* or wpackagist-theme/* package names, or has custom entries in repositories, applying this update can cause merge conflicts in that file. When you resolve the conflicts, keep your custom requirements and update the package names to the new wp-plugin/* and wp-theme/* names, or keep the WPackagist repository entry.

For assistance with managing merge conflicts, refer to our documentation on auto-resolving via the dashboard or manually resolving via the command line.

October 2, 2026

Pantheon has updated the default PHP version for the WordPress and WordPress (composer managed) upstreams to PHP 8.3, replacing the previous default of PHP 8.2.

New sites created from these upstreams use PHP 8.3. Existing sites that do not set php_version in their own pantheon.yml move to PHP 8.3 when they apply this upstream update.

Action required

Test the update before you deploy it to the Live environment. Apply it in Dev or a Multidev environment, confirm your plugins and theme work on PHP 8.3, then promote it.

If your site needs to stay on PHP 8.2, pin the version by setting php_version: 8.2 in your site's pantheon.yml before you apply the update. For steps, see Manage PHP Versions.

If you maintain a custom upstream, this change is not reflected in your pantheon.upstream.yml unless you update your fork from Pantheon's upstream.

October 1, 2026

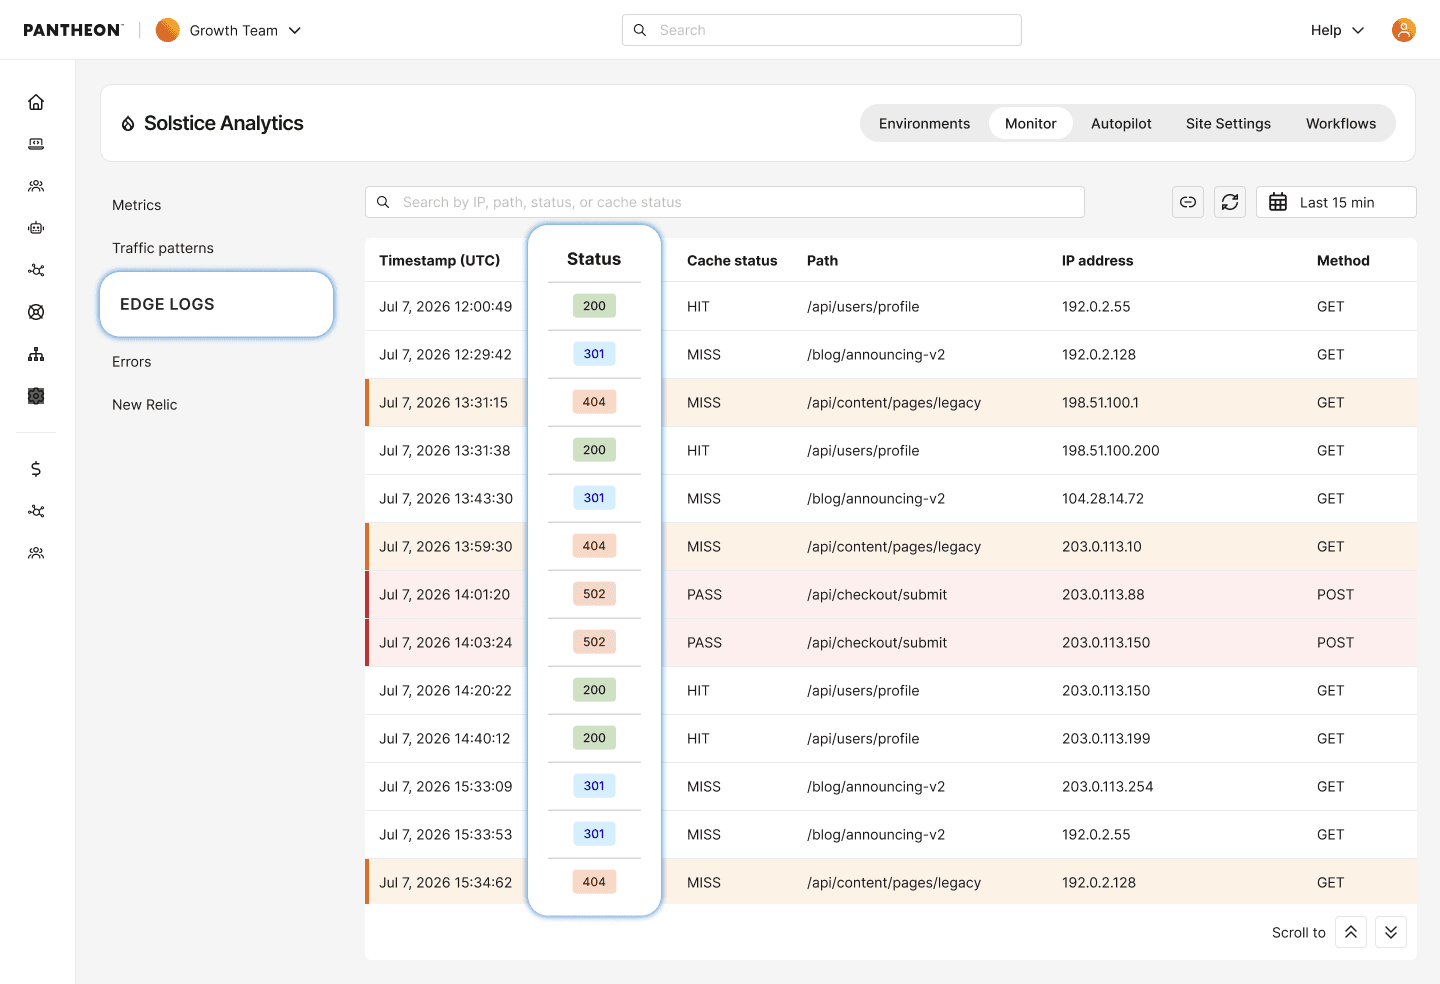
Pantheon now shows edge-level request activity in the dashboard, including cache statuses, ASNs, and response codes.

  • A new log explorer in the site dashboard shows how requests were handled at the edge, allowing request-specific investigation for up to 24 hours.
  • Search by HTTP status code, path, client IP, user agent, ASN, and time range.
  • Copy a permalink to a specific log view, including your search and time range, to share with a teammate for review.

For details, see related documentation.

edge access logs showing access logs

Information:
Note

This feature requires your site to be on our next-generation Global CDN. If your workspace includes sites still on our legacy Global CDN, your performance overview will only reflect migrated sites.

If you have not started or completed your migration, visit our documentation to get started.